About
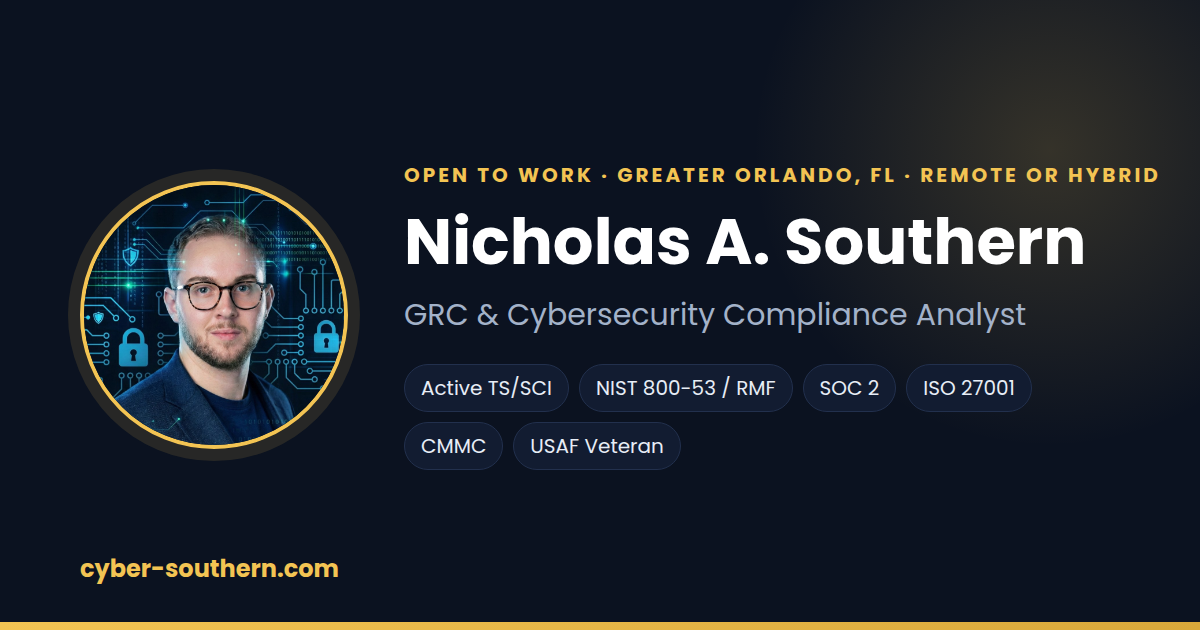
GRC and compliance analyst. Active TS/SCI. Greater Orlando, FL.
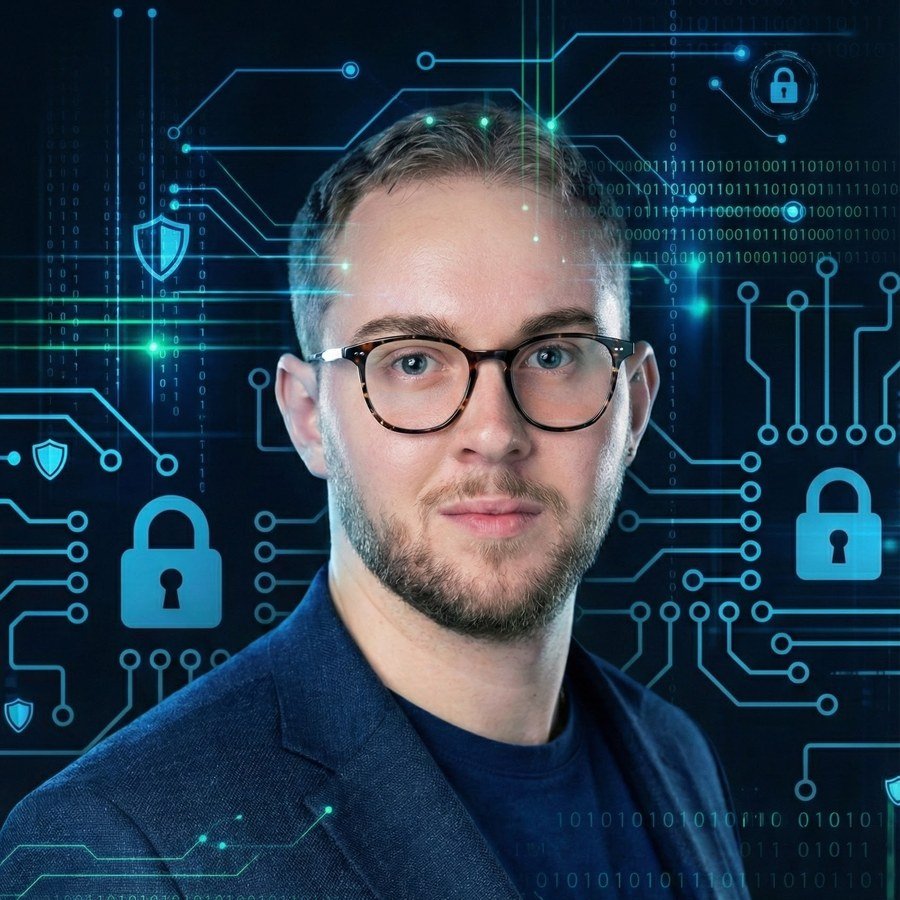
Personnel file
- Role
- GRC & Cybersecurity Compliance Analyst
- Current
- AI Cybersecurity Specialist, Invisible Technologies
- Clearance
- TS/SCI, active
- Location
- Greater Orlando, FL, remote-first
- Experience
- 6+ years across USAF, Lockheed Martin, and Invisible
- Education
- B.S. Cybersecurity & IA, WGU (December 2026)
- Fuel
- Black coffee, salt air
- Status
- Available, actively interviewing
Philosophy
Every alert, log line, and control narrative gets the same two questions: is it actionable, and can I prove it.
The short version
I started on a 24/7 watch floor at USAF Ramstein: four years of shift-based network defense for 3,000+ personnel across three Combatant Commands. More than a thousand Tier 1/2 incidents. When a zero-day dropped, my team hardened 241 systems across 11 sites inside 24 hours, and the RMF documentation I wrote held up with zero rework on the follow-up audit.
That last part turned out to be the career. Anyone can close a finding; the work that matters is proving it stays closed. At Lockheed Martin I moved fully into that world as a Senior Information Security Analyst on classified DoD programs. Control assessments, eMASS accreditation packages, POA&M governance, and continuous monitoring, with Python and PowerShell doing the evidence collection most teams still do by hand.
Today I work the newest attack surface there is: red-teaming frontier AI models at Invisible Technologies. Prompt injection, adversarial manipulation, and teaching models to reason correctly about the same NIST and ISO controls I’ve spent years implementing.
The through-line: compliance work built by someone who has actually worked the floor. I know which control failed behind an alert, and what the reporting obligation is. That operational time is why my paperwork survives audits.
Off hours
Salt water
Before the SIEM there was the sea. I spent two seasons teaching open-water sailing on Monterey Bay, and Florida keeps me within reach of the Atlantic. Best thinking happens near water.
Coffee
Black, early, and in quantities any reasonable dashboard would flag as anomalous. Running since 2019 with zero planned downtime.
Homelab
Zero trust experiments, Splunk tinkering, and CyberWarfare Labs challenges. The lab is where my opinions get tested before they show up in my writing.
Student
Finishing a WGU cybersecurity degree at night while working full-time. Graduation lands December 2026 and the countdown is very real.
How I work
01 · verify, then trust
Zero-trust isn’t a product, it’s a habit. Every claim gets checked against the evidence, including mine.
02 · signal over noise
Prioritize what’s actionable. A finding nobody can act on is decoration.
03 · build it audit-proof
Do the work so it survives the follow-up audit, not just the first one. Zero rework is the standard.
04 · translate up
Technical risk means nothing if leadership can’t act on it. Speak both languages.
Next
Full availability status, target roles, and highlights. Or go straight to the inbox.